NEXUSITY Book an IT audit
Managed IT Helpdesk · Monitoring · Security

One team owns your IT. All of it.

Nexusity runs the helpdesk, watches your servers and network, keeps devices patched and secure, and tells you plainly what to fix next. One contract, one monthly bill in ringgit.

11 minMedian first reply
1,284Tickets closed this quarter
30 minP1 response target
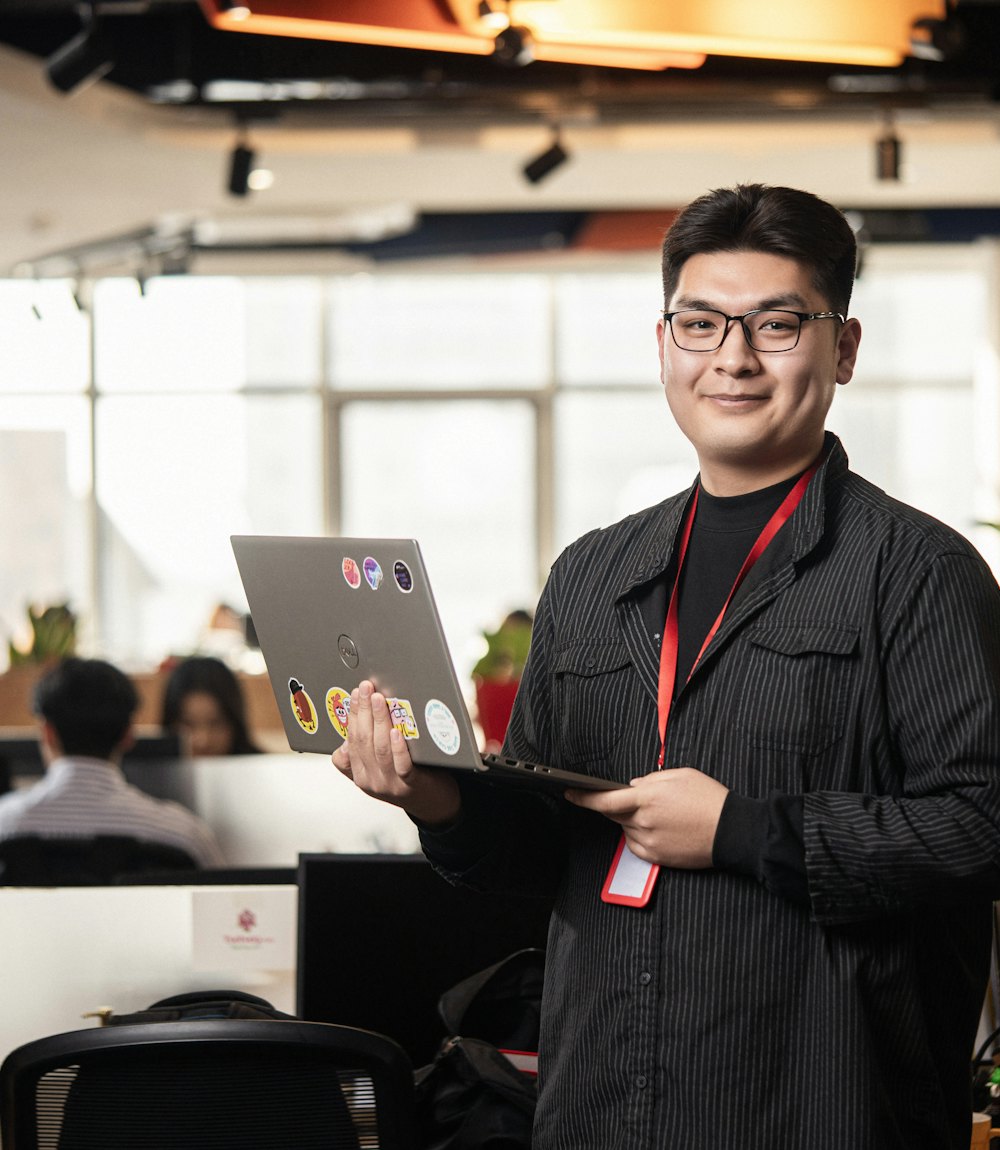
A Nexusity engineer holding a laptop in an open-plan office
SERVICE DESK · today monitoring

Sample feed for illustration. Client names removed.

For offices of 5 to 150 people in KL, Penang and JB One contract and one monthly invoice A named engineer for every client Response times written into the contract Engineers based in Malaysia, on-site when needed
§1 What we take over

The work nobody in your office should be doing.

Helpdesk

Staff email, call or WhatsApp us with anything from a locked account to a dead laptop. A named engineer picks it up.

reply ≤ 15 min

Monitoring

Servers, NAS, firewalls, Wi-Fi and backups are watched around the clock. Most alerts are fixed before anyone notices.

24 / 7

Security

Endpoint protection, patching, MFA and email filtering, set up once and checked every month.

patched ≤ 14 days

Devices & accounts

New joiners get a ready laptop and accounts on day one. Leavers lose access the same afternoon.

same day

Advice

A quarterly review of what is ageing, what is at risk, and what it will cost. Including when the answer is to wait.

every quarter
§2 The first 30 days

How we take over from your current setup.

WEEK 1 · AUDIT

We list everything

Every device, licence, password vault, backup and vendor contract. You get the list, even if you don't sign.

WEEK 2 · FIX

We close the gaps

Untested backups, shared admin passwords, unpatched machines. The urgent items are done first.

WEEK 3 · HANDOVER

We take the phone

Your staff get one support address and number. We collect access from the previous vendor.

WEEK 4 · REPORT

You see the numbers

The first monthly report: tickets, response times, risks found and what we did about them.

§3 Your other options

Three ways to run IT for a 40-person office.

OPTION A · HIRE IN-HOUSE

One good person is a single point of failure.

An IT executive in KL costs around RM 5,000 to 7,000 a month before EPF and SOCSO. When they are on leave, sick or resign, the knowledge leaves with them. One person also can't be an expert in networking, security and Microsoft 365 at once.

OPTION B · CALL A VENDOR WHEN IT BREAKS

Cheap until the month it isn't.

Ad-hoc support charges by the visit, so nobody is paid to prevent problems. The backup that silently failed in March is discovered in October, on the day you need it.

OPTION C · NEXUSITY

A team on a fixed fee, paid to keep things quiet.

For 40 users on the Managed plan, about RM 3,850 a month with SST. Several engineers know your setup, response times are written into the contract, and fewer tickets is how we make our margin.

We would rather spend an afternoon labelling your cables than a weekend restoring your server. Engineering team, Nexusity
§4 Questions

Asked on almost every first call.

Is there a minimum contract?

Monthly plans have a 3-month minimum. On a 12-month term we waive the RM 1,200 onboarding audit. Either way you can leave with 30 days' notice after the minimum, and we hand back every password and document.

Do you come on-site?

Yes. Managed includes one scheduled visit a month, Complete includes unlimited visits in the Klang Valley. Urgent visits outside your plan are RM 250 per visit within KL and Selangor.

We already have an IT person. Does this still make sense?

Often it does. We can act as their back-up and second line, take over monitoring and security, and leave them on the work that needs someone in the office.

What happens outside office hours?

Monitoring and P1 incidents (a server down, the whole office offline, a security breach) are covered 24/7 on Managed and Complete. Routine requests are handled 8:30 am to 6:30 pm, Monday to Friday.

Do you help with PDPA?

We set up the technical side: access controls, encryption, backups and breach logging, and give you the documentation. We are not lawyers, so we work alongside your legal adviser on the policy side.
Find out what would break first.

The audit takes about two hours on-site. You keep the findings whether or not you work with us.